Capcom Cyberattack Exposes 11.77M User Records
 James Whitfield
2 min read
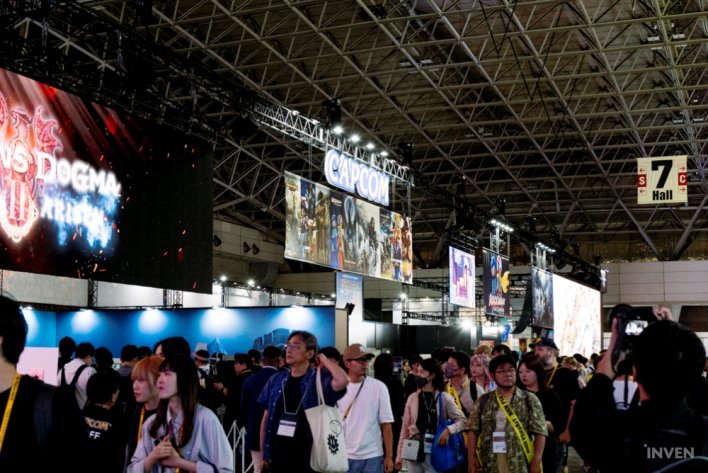
Capcom disclosed on October 22 that hackers breached its unified account system, compromising nearly 11.77 million user records worldwide. The attack on CAPCOM ID, a centralized login service for Capcom websites and select online games, exposed email addresses and system-generated account identifiers tied to those accounts.
The company revealed that 196 user accounts had their passwords forcibly changed by the attackers. Capcom has already reset passwords for all affected accounts and stated that no evidence suggests user-created passwords were stolen or exposed. Financial data remained secure, with credit card information untouched by the breach.
Beyond email addresses, the leaked system identifiers included account creation timestamps, most recent login dates and times, login frequency counts, and IP addresses from the final login session. In 43 cases, additional personal details were compromised: birth dates, gender, country or region, and user nicknames. Capcom did not break down the 11.77 million figure by country or region, making it impossible to determine how many Korean or other regional users were affected from the announcement alone.
Capcom detected suspicious unauthorized access attempts on October 19 and immediately blocked further access. After confirming the intrusion that same day, the company established an internal crisis response team on October 20. The company notified Japan's Personal Information Protection Commission and the Osaka Prefectural Police on October 21. The announcement did not specify when the initial breach occurred.
While CAPCOM ID services remain fully operational and gameplay is unaffected, Capcom warned users to remain vigilant against phishing attacks. Criminals may use the stolen email addresses to send fraudulent messages impersonating Capcom or affiliated organizations. The company advised users not to click suspicious links or download attachments from unexpected emails. Registered email addresses continue to function normally.
Capcom stated it has identified and closed the attack vector and is conducting an ongoing investigation into the full scope of the compromise. Affected users will be contacted individually as the investigation progresses. A dedicated toll-free hotline has been established in Japan for inquiries related to the incident. Users in Asia and Oceania outside Japan can contact Capcom's regional support team at info-asia@capcom.com. The company pledged to determine the breach's root cause, implement preventive measures, and provide updates through official channels as new information emerges.